
An EDR alternative with one evidence model.
We are honest: Dralvia's endpoint surface is in preview, not a replacement for a mature kernel-level EDR. Its difference is unification, host telemetry scored with the same engines and evidence as the rest of your security stack.
Endpoint security
See Dralvia in action.
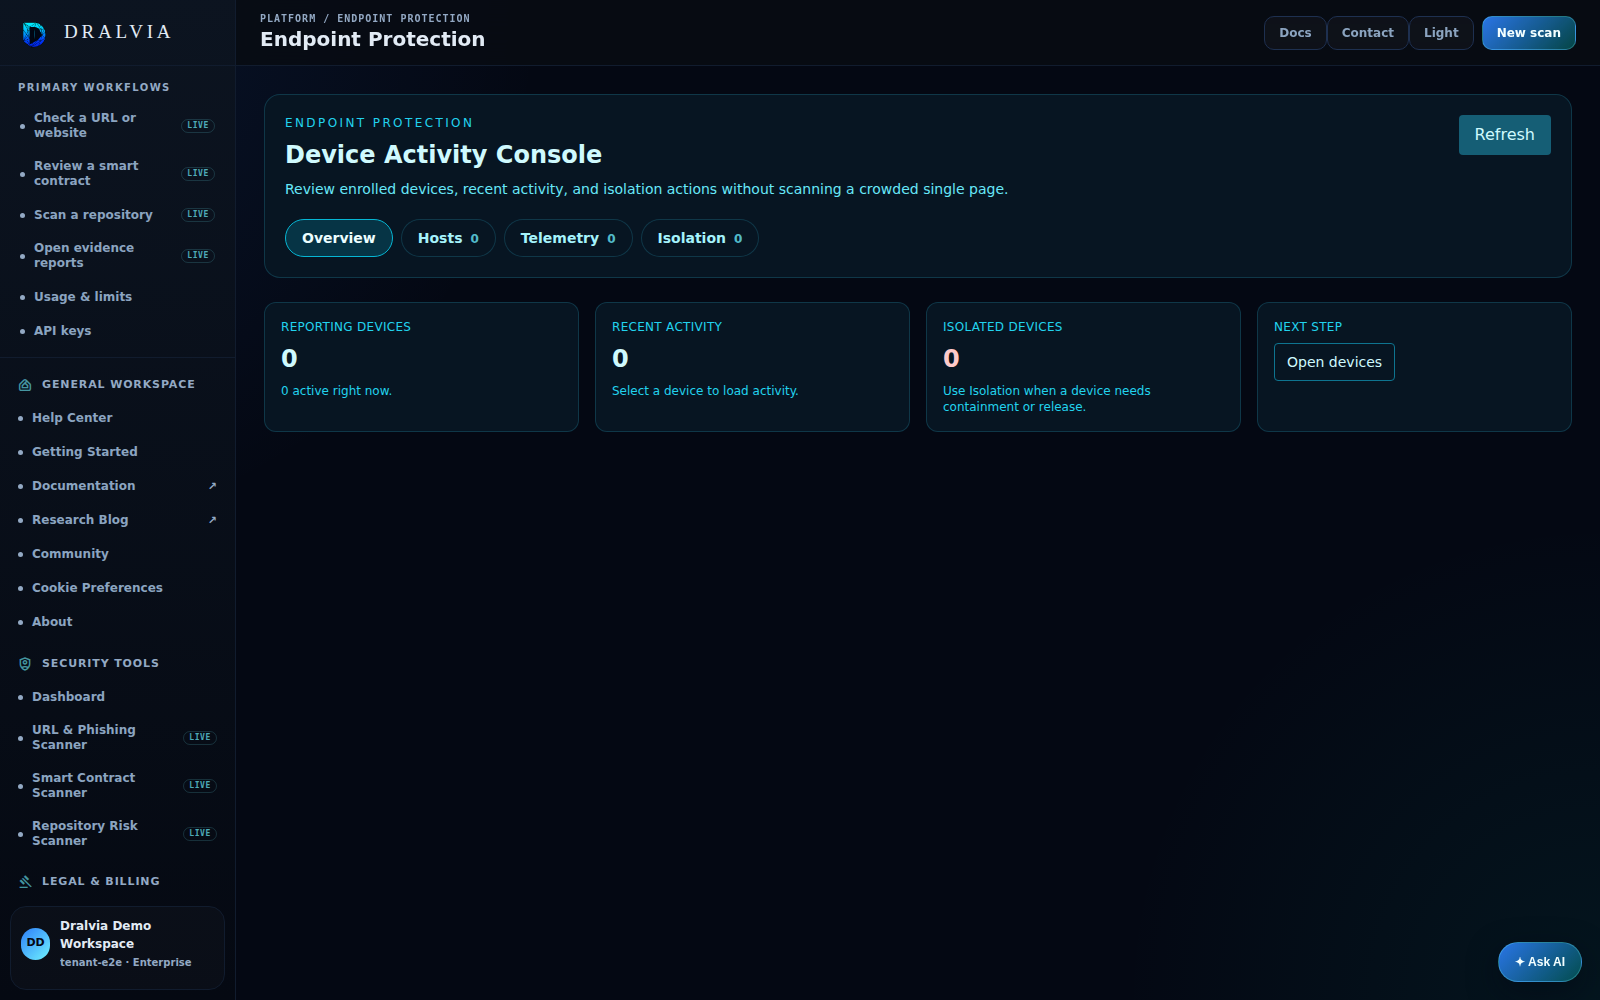
Review hosts and alerts, check agent readiness, and use the response actions included with your plan.
- Enroll the supported endpoint agent
- Review host and alert state
- Use guarded response actions
This preview shows the Dralvia workspace. Sign in to see your own scans, alerts, and activity.
Why teams add Dralvia alongside EDR.
One model across surfaces
Endpoint findings sit next to URL, contract, and repository verdicts, one place, one scoring model.
Network events scored
Outbound connections are scored against the same URL and domain verdicts as the scanners.
Shared EvidencePack
Endpoint findings export the same hash-pinned artifact as every other scanner.
Design-partner program
Shape coverage and rollout with us while the surface matures.
Honest answers.
Not today, it is in preview and best run alongside a mature EDR, bringing its telemetry into Dralvia's evidence model.
Try Dralvia as your Traditional EDR alternative.
Run it on your real work and see the verdict, the evidence, and the export.