
A phishing scanner alternative built for IR.
Most phishing checkers give a yes/no. Dralvia is the alternative that returns the 100+ signals behind the verdict, captures the redirect chain, fingerprints the kit, and exports an EvidencePack the next analyst can act on.
URL scanning
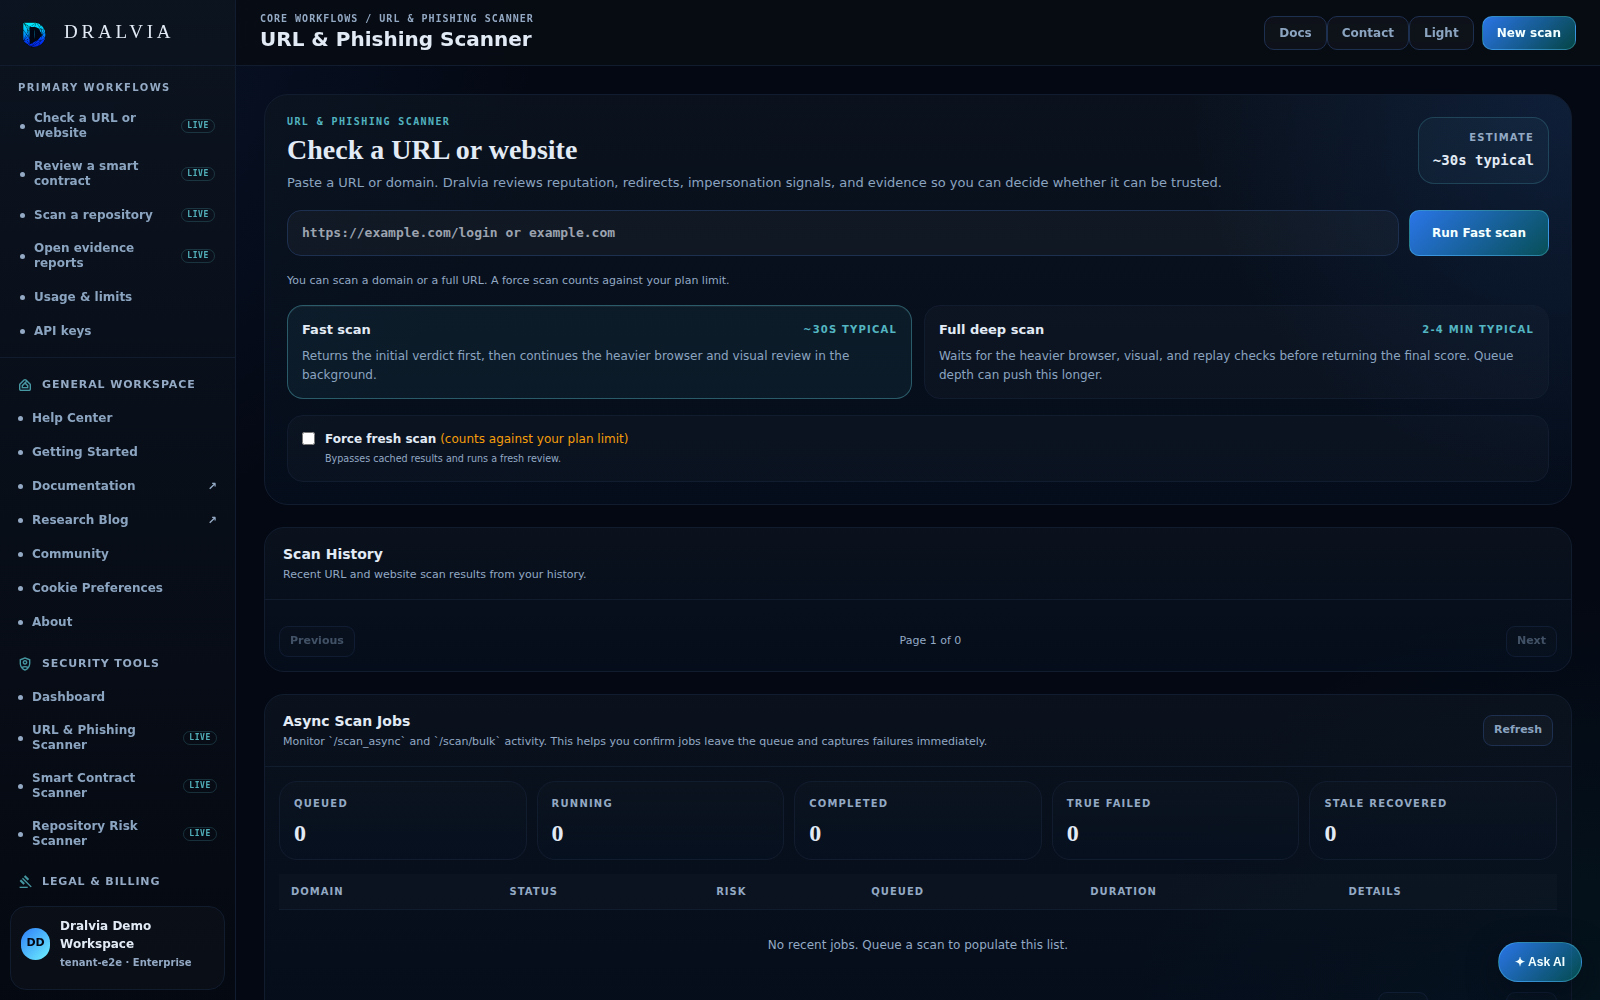
See Dralvia in action.
Submit a URL, choose the scan depth, and follow progress and results from one place.
- Paste a URL or domain
- Choose fast or deep review
- Follow the queue and result history
This preview shows the Dralvia workspace. Sign in to see your own scans, alerts, and activity.
What you gain switching to Dralvia.
Evidence behind the verdict
Every signal that fired and the engine that found it, not a single opaque score.
Redirect-chain unwrap
Shortlinks and JS hops are followed and re-scored to the final destination.
Kit fingerprinting
Recycled phishing kits and shared infrastructure cluster across domains.
Enforce it
Take the verdict to the browser extension and gateway to block, not just detect.
Exportable
PDF + JSON EvidencePack for the IR handoff.
Honest answers.
Yes, your first scan needs no account, and the free tier covers occasional manual triage.
Try Dralvia as your Phishing scanners alternative.
Run it on your real work and see the verdict, the evidence, and the export.