
A VirusTotal alternative that ends in a decision.
VirusTotal is a great signature aggregator. If you need a single verdict, the engines behind it cited inline, a private result, and an exportable EvidencePack you can hand to IR, Dralvia is the alternative teams move to.
URL scanning
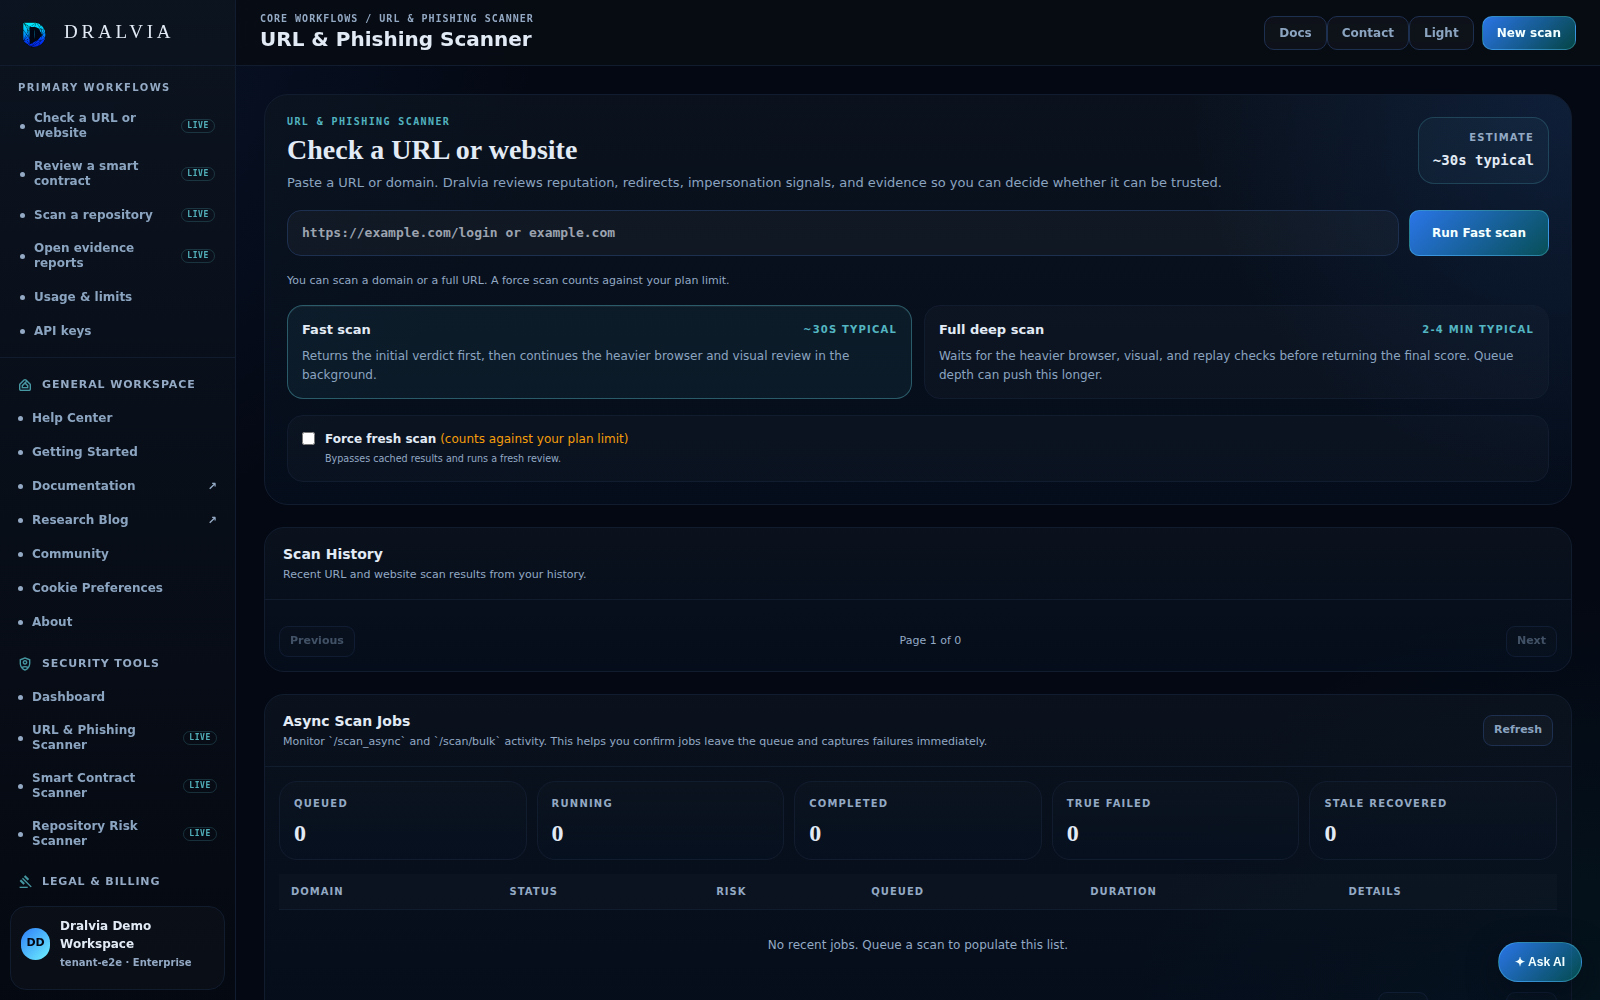
See Dralvia in action.
Submit a URL, choose the scan depth, and follow progress and results from one place.
- Paste a URL or domain
- Choose fast or deep review
- Follow the queue and result history
This preview shows the Dralvia workspace. Sign in to see your own scans, alerts, and activity.
What you gain switching from VirusTotal.
A decision, not a tally
One structured verdict with the contributing engines and their confidence, instead of counting how many engines flagged it.
Private by default
Workspace scans stay private to your workspace; anonymous free-tier scans are not indexed for the world to see.
Evidence that travels
Each verdict exports a hash-pinned EvidencePack (PDF + JSON) so the next analyst or auditor reproduces it.
Monitor mode
Watch a target and get alerted when the verdict drifts, useful for brand and infrastructure monitoring.
One engine, many surfaces
The same verdict model covers domains, contracts, and repositories, not just file and URL hashes.
Honest answers.
For URL and domain triage, yes, many teams switch. For a broad file-hash multi-engine matrix, VirusTotal remains strong; teams often run both and use Dralvia for the verdict and evidence layer.
Try Dralvia as your VirusTotal alternative.
Run it on your real work and see the verdict, the evidence, and the export.